US Extradites Teen in $8 Million Crypto Ransom Scheme
Peter Stokes, 19, has been charged in the US for allegedly taking part in a hacking group’s unsuccessful $8 million crypto ransom scheme.
Topic
344 articles found
Peter Stokes, 19, has been charged in the US for allegedly taking part in a hacking group’s unsuccessful $8 million crypto ransom scheme.
The new PamStealer Mac malware appears to be surprisingly clever while it harvests data and login credentials in the background.
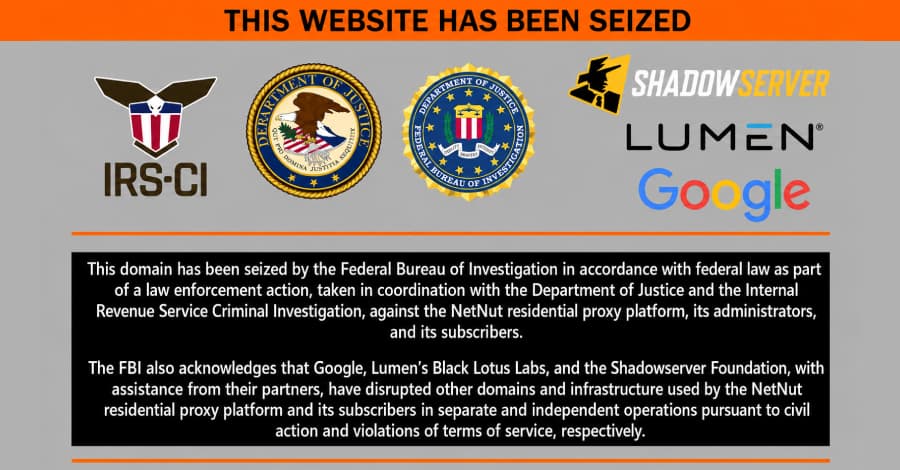
The tech giant said it disabled accounts and services used in NetNut-related malware command-and-control operations and shared technical intelligence on the group's infrastructure with law enforcement and industry partners to support broader enforcement efforts.
Improved institutional safeguards and stricter regulations have pushed the burdens of protection and risk reduction on to Australian businesses.
The discovery underscores the increased effort being poured into Mac infostealers.
Authorities are set to introduce stringent measures to prevent tampering with electric two and three-wheeler batteries. New regulations will mandate cybersecurity for imported e-rickshaws and scooters, while mobile apps capable of sabotaging existing vehicles, particularly those with Chinese batteri
After gaining a foothold in thousands of Fortinet firewalls, the attackers are starting to monetize that access, and are also piling on a Nextcloud zero-day bug.
Google has significantly degraded NetNut, one of the biggest networks that turns home devices into rented relays for other people's traffic. Working with the FBI, Lumen, and others, Google's Threat Intelligence Group (GTIG) said this week it had reduced the network's pool of usable devices by millio
Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain initial access. "Although tactics differ between affiliates, common patterns emerged in tradecraft through use of legitimate Remote Management and Mo
The ransomware campaign relies on basic social engineering and stretches across multiple regions, including the US, Europe, Middle East, and elsewhere.
Who Are The Gentlemen? Despite the impeccably polite name, there is nothing polite or refined about this particular gang of cybercriminals. Read more in my article on the Fortra blog.
Sources said that in the notice to Telegram, the government has asked the platform why it should be allowed to retain the username feature. On Wednesday, the Centre issued a notice to Meta over the username feature on WhatsApp, citing concerns that it could materially increase online fraud, phishing
This week’s security news is mostly about weak spots. Browsers, bots, sandboxes, AI systems, and email flows all show the same problem in different ways. Everything looks normal until someone tests a small gap and finds a way through. This is not one big break. It is small permissions, weak checks,
Researchers are also investigating the role of a suspected zero-day vulnerability.
Hackers are targeting NetScaler appliances using public PoC code to retrieve arbitrary memory content in the HTTP response. The post New CitrixBleed Vulnerability Exploited Immediately After Public Disclosure appeared first on SecurityWeek.
A top Democrat on the Senate's Intelligence Committee warned that the information accessed on a Homeland Security intelligence-sharing network may risk national security.
The security firm Bitdefender’s annual survey also found that U.S. companies were simultaneously more confident and more strained on cyber defense than foreign peers.
ConsentFix and ClickFix attacks steal Microsoft 365 tokens in seconds using fake prompts and OAuth flows. Learn how these MFA bypass tactics work and how to defend against them. [...]
Available today, ExpressKeys now delivers more secure sharing, passkey support, and improved cross-device management.
Researchers say credentials harvested from hundreds of thousands of FortiGate firewalls are being used to facilitate ransomware attacks by the INC and Lynx operations. The post FortiBleed Campaign Linked to INC, Lynx Ransomware Attacks appeared first on SecurityWeek.