Kimwolf Botmaster Arrested: A Turning Point in IoT Security
Canadian authorities on Wednesday arrested a 23-year-old Ottawa man on suspicion of building and operating Kimwolf, a fast spreading Internet-of-Things botnet that enslaved millions of devices for use in a series of massive distributed denial-of-service (DDoS) attacks over the past six months. Krebs
Key Insights
10 editorial insights.
The arrest of the 23-year-old Ottawa man, identified as 'Dort', underscores the increasing vulnerability of Internet-of-Things (IoT) devices, which are often inadequately secured. With millions of devices compromised, this incident highlights the need for manufacturers to adopt stricter security protocols and for consumers to prioritize device security to mitigate such risks.
Kimwolf's rapid spread indicates a troubling trend in the cybercrime landscape, where botnets are evolving to exploit the sheer volume of IoT devices. The fact that these attacks have escalated over the past six months suggests an organized effort to harness vast computing power for nefarious purposes, raising alarms about the scale of future DDoS attacks.
The transatlantic cooperation between Canadian authorities and other international law enforcement agencies demonstrates a significant shift in how cybercrime is tackled globally. This collaborative effort is crucial, as cybercriminals often operate across borders, making coordinated actions essential for effective law enforcement and deterrence.
As a botmaster, Dort's operational model reflects the growing trend of cybercriminals commodifying their skills, potentially selling access to the Kimwolf botnet to other malicious actors. This commercialization of cybercrime not only amplifies the threat but also complicates law enforcement efforts, as various players in the cyber underworld become interconnected.
The massive scale of Kimwolf's DDoS attacks, fueled by compromised IoT devices, serves as a wake-up call for businesses and organizations reliant on online services. High-profile outages can result in significant financial losses and reputational damage, pushing companies to invest more heavily in cybersecurity measures to protect against such vulnerabilities.
This case highlights the pressing need for regulatory frameworks around IoT device security, as many devices lack basic security features. Policymakers should consider implementing mandatory security standards for IoT manufacturers to prevent future incidents and protect consumers from being unwitting participants in cybercrime.
Dort's arrest may serve as a deterrent to other aspiring botmasters, but it also raises questions about the cybersecurity ecosystem's resilience. As law enforcement successfully disrupts one botnet, it is likely that new groups will emerge, indicating a perpetual cycle of cybercrime that requires ongoing vigilance and adaptation from security professionals.
The Kimwolf incident reflects the increasing sophistication of cybercriminals in leveraging everyday technology for malicious purposes. As more devices become interconnected, the potential attack surface grows, necessitating a broader understanding of cybersecurity risks and encouraging organizations to adopt a proactive rather than reactive approach to defense.
The rise of botnets like Kimwolf showcases the critical need for consumer education on the importance of securing IoT devices. Many users remain unaware of the risks associated with default passwords and outdated firmware, emphasizing the role of public awareness campaigns in enhancing overall cybersecurity hygiene.
Finally, the fallout from the Kimwolf botnet serves as a reminder for technology companies to prioritize security in their product development lifecycle. Companies like Amazon and Google, which dominate the IoT space, must take proactive steps to ensure their devices are not just innovative but also secure, protecting consumers and their networks from potential exploitation.
The recent arrest of a 23-year-old man in Ottawa for operating the Kimwolf botnet marks a significant moment in cybersecurity, especially in the realm of Internet of Things (IoT) vulnerabilities. This botnet, which compromised millions of devices, underscores the urgent need for stronger security measures as cyber threats evolve and proliferate.
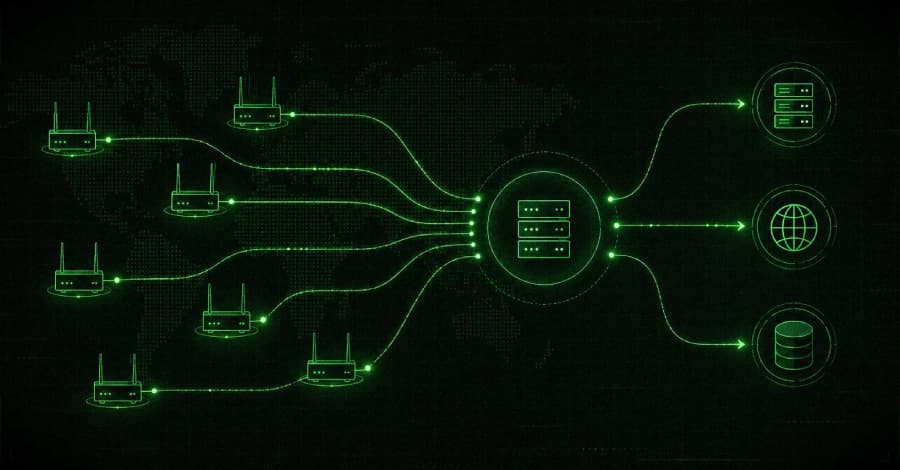
Kimwolf leveraged a range of IoT devices, turning them into a coordinated army for DDoS attacks. The botnet utilized known vulnerabilities in devices such as smart cameras, routers, and home assistants, exploiting weak passwords and outdated firmware. This approach allowed Kimwolf to generate massive traffic volumes directed at targeted websites, causing significant downtime and service disruptions. The technical architecture of Kimwolf involved decentralized command-and-control servers, making it harder to dismantle and trace.
In the broader cybersecurity landscape, the rise of IoT botnets like Kimwolf is indicative of a worrying trend. As IoT device adoption surges, so do the security challenges. Industry analysts report that the global DDoS mitigation market is expected to reach $3.8 billion by 2026, reflecting the urgent demand for solutions to counteract these threats. Competitors in the cybersecurity space are ramping up their offerings, focusing on proactive measures and real-time threat detection to safeguard against such attacks.
For India, the implications of the Kimwolf incident are particularly pressing. As a rapidly growing market for IoT devices, Indian companies must prioritize security in their product designs. Enterprises like Reliance Jio and Airtel are expanding their IoT services, potentially facing increased scrutiny over their security practices. Additionally, Indian developers and cybersecurity firms hold a critical role in creating robust solutions to safeguard against similar threats, especially as the country becomes a hub for IoT innovation.
Key Highlights
- Arrest reflects the growing focus on IoT security enforcement
- Kimwolf was capable of enslaving millions of IoT devices for DDoS attacks
- DDoS mitigation market projected to grow to $3.8 billion by 2026
- Consumers and businesses using IoT devices will benefit from heightened security awareness
- Expect increased regulatory scrutiny and security standards in the IoT space
Real-World Impact
The immediate fallout from the arrest will likely affect cybersecurity professionals, IoT developers, and device manufacturers. Increased regulatory pressures may lead to new job roles focused on security compliance and IoT architecture. Companies will need to invest in security audits and engineer teams to develop more resilient products, especially in sectors like smart home technology and connected automotive systems.
Why This Matters
This incident highlights a strategic shift in how cybersecurity is approached in the IoT sector. As threats become more sophisticated, CTOs and developers must adopt a mindset of proactive security, integrating best practices into the development lifecycle. This includes regular updates, strong authentication protocols, and comprehensive incident response plans to combat evolving cyber threats.
As the dust settles from the Kimwolf arrest, one key aspect to watch will be how regulators respond to the ongoing IoT security crisis. The implementation of stricter regulations around IoT security may soon become a reality, pushing manufacturers to innovate with security as a priority.
Found this useful? Share it!