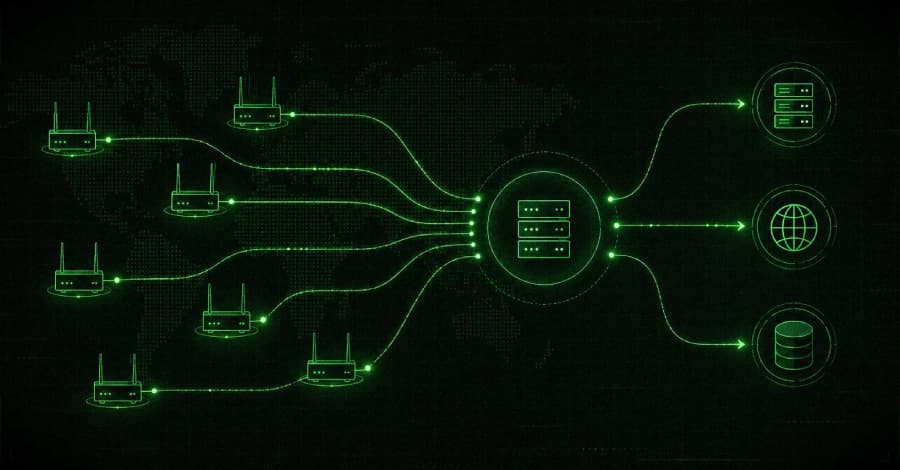
A new malware family is turning forgotten home routers into a distributed reconnaissance and proxy network, not the DDoS botnet these devices usually end up in. QiAnXin's XLab calls it AryStinger and counts at least 4,300 infected routers, a total it says is still rising. The distinction matters. Ar
A new cybersecurity threat has emerged as cybercriminals have reportedly hijacked over 4,300 home routers across India to create a stealthy proxy network. This development highlights a significant shift in how compromised devices are being utilized, moving away from traditional DDoS botnets to more insidious reconnaissance operations. Understanding this threat is vital for both users and enterprises, particularly in a digitally connected landscape like India.
The malware, identified as AryStinger by QiAnXin's XLab, enables hackers to commandeer infected routers covertly. Once compromised, these routers serve as conduits for distributing malicious traffic and gathering sensitive information without the owner's knowledge. The technical workings involve exploiting vulnerabilities in the router firmware, often targeting devices that have not been updated with the latest security patches. This allows hackers to maintain a persistent presence while remaining under the radar.
This incident underscores a broader trend in cybersecurity where home routers are increasingly viewed as strategic assets for cybercriminals. Unlike conventional DDoS-focused botnets, the AryStinger proxy network offers more complex capabilities, such as stealthy data exfiltration and reconnaissance. The global cybersecurity market is witnessing a surge in sophisticated malware targeting Internet of Things (IoT) devices, with projections estimating a 25% growth in related threats by 2025.
In India, the impact of the AryStinger malware could be profound. As the country rapidly embraces digital transformation, millions of households rely on home routers for internet access. Indian ISPs and security firms must prioritize user education and security measures to mitigate risks. Additionally, startups focusing on cybersecurity solutions may find new opportunities to address these vulnerabilities, potentially influencing the growth of the cybersecurity sector in India.
Key Highlights
- Action verb — hackers exploit routers for malicious purposes
- Technical specifications — AryStinger utilizes unpatched vulnerabilities
- Market impact — 25% growth in IoT-related cyber threats expected
- Who benefits most — cybersecurity startups and ISPs enhancing security protocols
- What to expect next — increased scrutiny on home router security measures
Real-World Impact
The immediate effect of the AryStinger malware is a heightened risk for home users, particularly those in sectors like e-commerce and finance where online transactions are prevalent. IT managers and security professionals must remain vigilant, as compromised routers could lead to data breaches and financial losses. Users should also be aware of the importance of securing their home networks.
Why This Matters
This situation reflects a critical shift in the cyber threat landscape, emphasizing the importance of securing all networked devices, not just traditional computers. CTOs and developers should reassess their security protocols and consider implementing multi-layered defenses to safeguard against such vulnerabilities. Proactive measures, including regular firmware updates and robust network monitoring, are essential.
As the cybersecurity landscape evolves, the rise of sophisticated malware like AryStinger serves as a wake-up call for users and enterprises alike. Keeping an eye on the advancements in malware tactics and developing adaptive security strategies will be crucial in the coming months.
Found this useful? Share it!