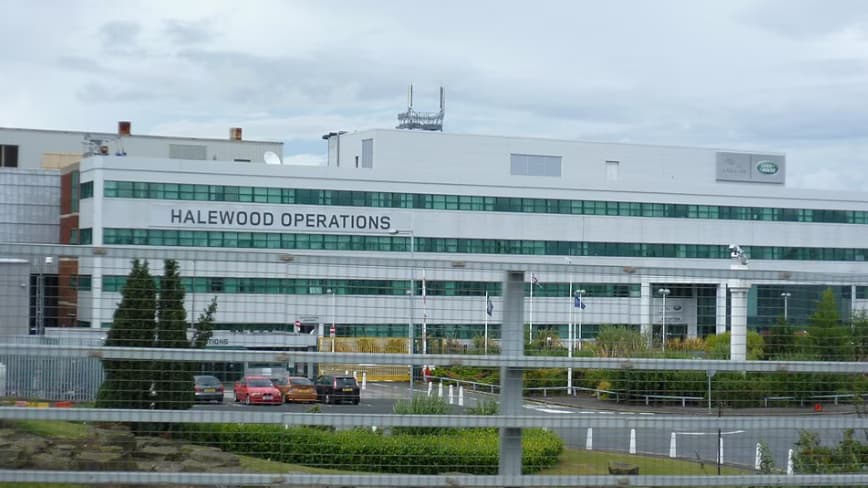
Russian hackers were behind last year’s devastating cyberattack on Jaguar Land Rover, according to a New York Times investigation published Thursday. The breach, which began on 31 August 2025, shut down production across JLR’s factories for nearly six weeks and cost the British economy an estimated
Key Insights
10 editorial insights.
The cyberattack on Jaguar Land Rover (JLR) by Russian hackers, which resulted in the shutdown of production for nearly six weeks, underscores the vulnerability of critical manufacturing sectors to cyber threats. This incident highlights the immediate need for robust cybersecurity measures in industries reliant on technology-driven production processes, as even short-term disruptions can lead to substantial financial losses.
Key players in this incident include Jaguar Land Rover and the Russian hacking group believed to be behind the attack, which emphasizes the growing sophistication of cybercriminal organizations. JLR's position as a leading luxury car manufacturer makes it a significant target, and its experience with this breach could influence how other companies in the automotive sector approach their cybersecurity frameworks.
This cyberattack serves as a strategic wake-up call for the automotive industry, which is increasingly dependent on digital technologies for operations and customer engagement. As manufacturers adopt more connected systems and automation, the risks associated with cyber threats become more pronounced, necessitating an industry-wide reassessment of cybersecurity protocols.
The estimated $2.5 billion cost to the UK economy reflects the broader implications of cyberattacks on business operations, particularly in the automotive sector. Companies like JLR, which operate on thin margins, may face significant challenges in recovering from such losses, potentially impacting their ability to invest in innovation and growth.
This incident aligns with a broader trend in the past 12-24 months where cyberattacks on major corporations have surged, indicating a growing threat landscape. As organizations transition to more digitally integrated operations, the frequency and severity of these attacks are likely to continue increasing, prompting a reevaluation of security investments across industries.
The global automotive cybersecurity market is projected to reach $2 billion by 2026, growing at a CAGR of 25% from 2021. Incidents like the JLR attack emphasize the urgency for companies to invest in advanced cybersecurity solutions as part of their operational strategy to protect against significant financial losses and reputational damage.
The JLR cyberattack raises critical questions about the adequacy of current cybersecurity measures in place within the automotive sector. Companies may now face increased pressure to demonstrate their resilience against such threats, which could lead to regulatory scrutiny and the need for improved compliance with data protection regulations.
Competitors in the automotive industry are likely to respond by strengthening their cybersecurity investments and protocols to mitigate risks highlighted by the JLR incident. Companies such as BMW and Mercedes-Benz may enhance their collaboration with cybersecurity firms to develop more robust defense mechanisms against potential attacks, setting new industry standards.
Over the next 6-12 months, it will be important to monitor developments in cybersecurity regulations, particularly in the UK, as the government may implement stricter guidelines for data protection and incident response. Additionally, advancements in cybersecurity technologies, such as AI-driven threat detection, will be critical in improving industry resilience against future attacks.
For technology professionals and investors, the JLR incident signifies the increasing importance of cybersecurity within the tech landscape. As the costs associated with breaches rise, there is a growing opportunity for innovation in cybersecurity solutions, making it a lucrative area for investment and career development in the coming years.
The recent revelation that Russian hackers orchestrated the cyberattack on Jaguar Land Rover (JLR) last year underscores the growing threat of cybercrime to major industries. This breach, which halted production for nearly six weeks, incurred an estimated $2.5 billion loss to the British economy. As countries and companies grapple with similar threats, understanding the implications has never been more urgent.
The cyberattack on JLR, commencing on August 31, 2025, was characterized by sophisticated techniques that breached the company's cybersecurity defenses. Hackers exploited vulnerabilities in JLR's production systems, effectively crippling operations across multiple factories. The breach reportedly involved ransomware, which encrypted critical data and demanded payment for its release. This attack highlights the increasing complexity of cyber threats, where hackers leverage advanced methods, including social engineering and zero-day exploits, to infiltrate corporate networks.
In the broader automotive industry, JLR is not alone in facing such threats. Major competitors are also investing heavily in cybersecurity infrastructure to protect against similar incursions. The shift towards connected vehicles and smart manufacturing processes has increased the vulnerability of companies to cyberattacks. According to industry reports, the global automotive cybersecurity market is projected to grow significantly, driven by rising incidences of cyber threats and regulatory pressures for enhanced security measures.
In India, the impact of such cyber incidents extends to the burgeoning automotive sector, which includes companies like Tata Motors and Mahindra & Mahindra. As Indian manufacturers expand their digital capabilities, they must prioritize cybersecurity as a critical component of their operational strategy. The Indian IT services sector, including firms specializing in cybersecurity solutions, stands to benefit as automotive companies seek to bolster their defenses against similar threats.
Key Highlights
- Russian hackers exploited vulnerabilities in JLR's systems.
- Attack involved ransomware that encrypted critical data.
- The incident cost the UK economy approximately $2.5 billion.
- Indian automotive firms must enhance cybersecurity measures.
- Expect increased investment in cybersecurity solutions across industries.
Real-World Impact
The immediate effects of the JLR cyberattack are profound, impacting not only the company's workforce but also the broader automotive supply chain. Job roles in cybersecurity, IT management, and production operations are now under scrutiny. Industries reliant on manufacturing and technology need to reassess their cybersecurity frameworks to mitigate risks associated with such attacks.
Why This Matters
This incident exemplifies a larger strategic shift in how industries perceive and manage cybersecurity risks. CTOs and developers must adopt a proactive stance, integrating robust cybersecurity measures into their operational frameworks. This includes regular audits, employee training, and investment in advanced security technologies to stay ahead of evolving threats.
As the landscape of cyber threats continues to evolve, staying informed about emerging vulnerabilities and attack vectors is crucial. One key area to watch is the development of international cybersecurity frameworks aimed at protecting critical industries, particularly in the automotive sector.
Found this useful? Share it!