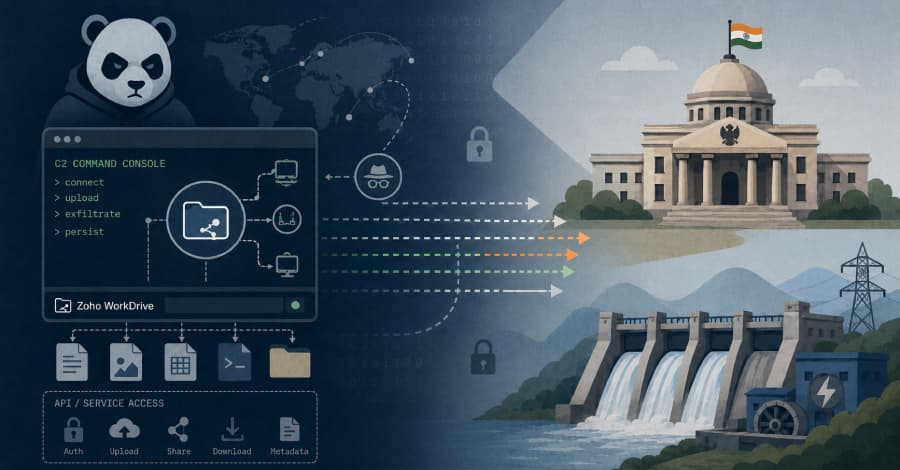
The China-aligned espionage group Mustang Panda is running two campaigns against the Indian government and hydropower targets, deploying new malware and turning a legitimate cloud service into its command channel. Acronis Threat Research Unit found active compromises inside Indian government network
Key Insights
10 editorial insights.
Mustang Panda's utilization of Zoho WorkDrive as a command channel signifies a concerning evolution in cyber-espionage tactics, blurring the line between legitimate services and malicious activities. By leveraging a trusted platform, the group enhances its stealth, making detection by cybersecurity measures increasingly difficult and posing immediate threats to sensitive government data.
The Acronis Threat Research Unit's findings underscore the importance of vigilance from cybersecurity firms and highlight the growing capabilities of state-sponsored actors like Mustang Panda. Zoho, a significant player in the cloud services market, must respond promptly to mitigate risks associated with its platform being exploited, as it could damage its reputation and customer trust.
This incident emphasizes the strategic importance of cybersecurity not only for government entities but also for software providers and cloud service platforms. As nation-state actors evolve their strategies, the industry must prioritize enhanced security measures, potentially leading to increased investments in cybersecurity solutions and innovations across the sector.
The exposure of Zoho WorkDrive's vulnerabilities could lead to significant business implications, particularly for Indian government agencies relying on this service for sensitive operations. If compromised data is leaked or manipulated, it could result in financial losses, reputational damage, and disruptions in governance, affecting millions of citizens.
The incident aligns with a broader trend of increasing cyberattacks against governmental and infrastructure targets, a focus that has accelerated over the past 12-24 months. As geopolitical tensions rise, the frequency and sophistication of cyber-espionage efforts by state-sponsored groups like Mustang Panda are likely to increase, indicating a need for robust cybersecurity frameworks.
The global cybersecurity market is projected to grow from approximately $200 billion in 2023 to over $300 billion by 2026, reflecting an annual growth rate of about 10%. This growth is driven by rising cyber threats such as those posed by groups like Mustang Panda, making it imperative for organizations to bolster their defenses against similar attacks.
This situation raises critical questions around the security of legitimate software used in sensitive sectors, highlighting the need for enhanced vetting and monitoring of cloud services. Additionally, the risks of supply chain vulnerabilities are amplified, prompting organizations to reassess their reliance on third-party applications in the face of sophisticated cyber threats.
In response to these developments, competitors in the cybersecurity space, such as CrowdStrike and Palo Alto Networks, may enhance their offerings or develop new solutions specifically designed to detect and mitigate threats linked to legitimate service misuse. This could lead to an arms race in cybersecurity capabilities as firms seek to differentiate themselves in a crowded market.
Over the next 6-12 months, key milestones to watch include potential regulatory changes regarding data security standards for cloud services, particularly in light of rising cyber threats. Additionally, the response measures taken by Zoho and other cloud providers to enhance their security protocols will be crucial in shaping the industry's landscape.
For technology professionals and investors, the incident highlights the critical importance of robust cybersecurity measures as a fundamental pillar of business strategy. As investments in cybersecurity solutions become more prominent, understanding the implications of these evolving threats will be essential for safeguarding assets and ensuring long-term viability in the tech landscape.
The Indian government has been compromised by the Mustang Panda APT group, which utilized Zoho WorkDrive as a covert command channel. This breach highlights significant vulnerabilities in national cybersecurity, particularly as cyber threats from state-aligned groups escalate. The implications of this incident underscore an urgent need for enhanced security protocols in sensitive sectors.
Mustang Panda's operations involve sophisticated tactics including the deployment of new malware and the exploitation of legitimate cloud services like Zoho WorkDrive. By leveraging these platforms, the group can hide its activities within typical user behaviors, complicating detection efforts. Security researchers from Acronis identified ongoing compromises within the Indian government’s network, indicating a focused effort to gather intelligence on critical infrastructure, particularly hydropower assets.
This incident reflects a broader trend in cybersecurity where state-sponsored groups are increasingly targeting government entities and essential services. The use of trusted platforms for malicious purposes demonstrates a shift in tactics, compelling companies to reassess their security measures. The global cybersecurity market is projected to reach $345.4 billion by 2026, emphasizing the escalating need for robust defense systems against such threats.
Within India’s tech ecosystem, this breach could have lasting repercussions, particularly for sectors involved in critical infrastructure and cloud services. Companies like Zoho, which provide essential tools for government operations, may need to enhance their security protocols to regain trust. Additionally, Indian cybersecurity firms may see increased demand for their services as organizations look to bolster defenses against APT groups targeting sensitive data.
Key Highlights
- Mustang Panda exploited Zoho WorkDrive for command and control.
- New malware indicates advanced capabilities of APT groups.
- Cybersecurity market projected at $345.4 billion by 2026.
- Companies providing security solutions are likely to benefit most.
- Expect stronger cybersecurity measures in government sectors soon.
Real-World Impact
Immediate effects of this breach will be felt across various government departments and critical infrastructure sectors. Cybersecurity professionals, IT staff, and government officials will need to address vulnerabilities in their systems. As the threat landscape evolves, job roles focused on security protocols and incident response will become increasingly pivotal.
Why This Matters
This incident signifies a strategic shift in cyber warfare tactics, showcasing how state-aligned groups can infiltrate even trusted platforms. For CTOs and developers, this highlights the necessity of implementing multi-layered security strategies, including regular audits and threat assessments to safeguard sensitive data from sophisticated attacks.
As the Indian government strengthens its cybersecurity posture in response to this incident, watch for potential collaborations with cybersecurity firms to enhance defenses. The outcomes of these efforts will be crucial in determining the resilience of India’s digital infrastructure against future threats.
Found this useful? Share it!