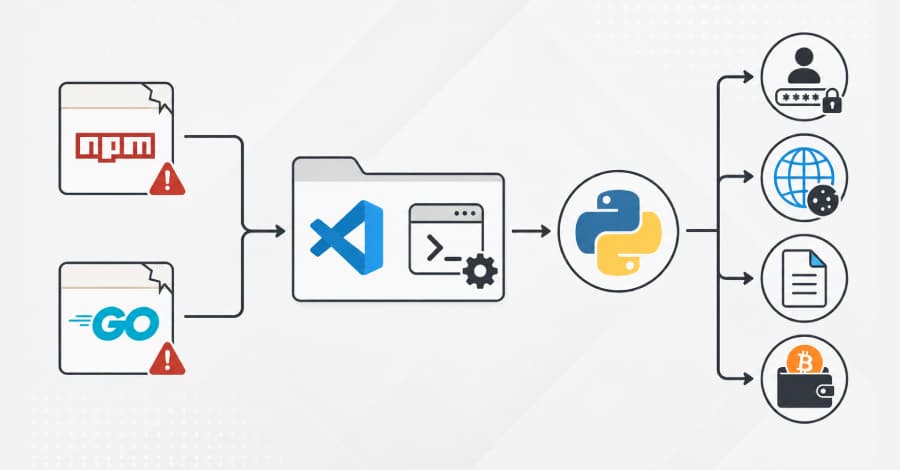
Cybersecurity researchers have uncovered two hijacked npm packages and a cluster of Go packages that are designed to deploy a Python-based information stealer on compromised Windows, Linux, and macOS hosts. "This attack avoids the most common npm execution paths through lifecycle scripts, perhaps in
Key Insights
10 editorial insights.
The discovery of hijacked npm and Go packages that deploy a Python-based infostealer highlights a critical vulnerability in widely-used package registries. This incident is significant as it underscores the growing sophistication of cyber threats, which can bypass traditional security measures and compromise systems across multiple operating environments, including Windows, Linux, and macOS.
Key players in this incident include the maintainers of the hijacked npm and Go packages, as well as major platforms like npm and GitHub, which host these repositories. Their response to this breach will be crucial in restoring trust among developers, especially given the popularity of npm, which boasts over 1.5 million packages, making it a prime target for exploitation.
This development is strategically important as it represents a shift in attack vectors, where adversaries leverage package management tools instead of more conventional malware delivery methods. Such tactics can lead to increased adoption of stricter package validation measures and security frameworks within the software development lifecycle, ultimately reshaping how developers approach security.
The direct business impact of this attack could be significant for companies relying on these compromised packages. Developers may face increased scrutiny and potential downtime, while businesses could incur costs associated with incident response, system recovery, and damages to their reputation, which can be detrimental in competitive tech markets.
This incident aligns with a broader trend of escalating cyber threats targeting open-source software ecosystems, which have become increasingly popular. Over the past 12 months, the adoption of open-source tools in enterprise environments has surged, with 90% of organizations using some form of open-source software, raising the stakes for security vulnerabilities.
In terms of quantitative context, the global cybersecurity market is projected to grow from $217 billion in 2021 to $345 billion by 2026, reflecting a compound annual growth rate (CAGR) of 10.2%. The increase in cyber incidents like this one could further drive investment in cybersecurity solutions, as organizations seek to mitigate risks associated with open-source dependencies.
This incident raises primary risks regarding the integrity of third-party packages and the potential for further exploitation of existing vulnerabilities. Unresolved questions include how many additional compromised packages might exist and how developers can better protect their code and environments against such sophisticated attacks.
Competitors in the cybersecurity and software development spaces will likely ramp up their efforts to enhance package security protocols, potentially leading to the development of new tools aimed at identifying and mitigating risks associated with third-party dependencies. Companies like Snyk and Sonatype may see increased demand for their solutions as developers seek to bolster security.
In the next 6-12 months, significant milestones to watch include potential regulatory actions aimed at improving software supply chain security. Initiatives like the U.S. government's executive order on cybersecurity could lead to mandatory security standards for software development, influencing how packages are managed and maintained across the industry.
Ultimately, the significance of this breach extends to technology professionals and investors, highlighting the urgent need for robust security practices in software development. As the landscape evolves, those who adapt to these emerging threats will not only protect their organizations but also position themselves as leaders in an increasingly security-conscious market.
Recent discoveries reveal that two npm packages and several Go packages have been hijacked to deploy a Python-based information stealer across various operating systems, including Windows, Linux, and macOS. This incident highlights a growing threat in cyber security, particularly for developers who rely on package management systems. Understanding this breach is crucial for organizations to bolster their security protocols against similar attacks.
The technical mechanics behind this malware involve the hijacking of npm and Go packages, which are commonly used in software development. Once these compromised packages are installed, they can execute malicious scripts that extract sensitive information without triggering typical security measures. This attack sidesteps common npm execution paths, making detection challenging. The deployment of the Python-based information stealer suggests that attackers have evolved their tactics to exploit trusted development environments, emphasizing the need for enhanced vigilance in code sourcing.
In the broader tech landscape, the use of package managers like npm and Go is fundamental to modern software development, raising concerns about the reliability of third-party dependencies. This incident is not isolated; it reflects a trend where cybercriminals increasingly target supply chain vulnerabilities. As more developers rely on open-source packages, the risk of such attacks grows. Companies need to prioritize cybersecurity measures, particularly in how they verify and manage dependencies.
For the Indian tech ecosystem, this incident poses significant risks, especially for startups and developers who frequently leverage open-source libraries in their projects. Major tech hubs like Bengaluru, where many software firms operate, could see heightened scrutiny of their security protocols. Indian developers, often under pressure to deliver quickly, may overlook security practices, making them prime targets for such malware attacks. This situation calls for increased awareness and education regarding secure coding practices among developers in India.
Key Highlights
- Cybersecurity researchers identify hijacked npm and Go packages.
- Malware deploys a Python information stealer on multiple OS.
- Rising dependence on open-source packages increases the risk of attacks.
- Developers and startups are most vulnerable due to rapid deployment cycles.
- Expect heightened security measures and scrutiny in coding practices.
Real-World Impact
Immediate effects of this malware discovery are being felt across various sectors, particularly among software developers and cybersecurity professionals. Developers may find themselves needing to reassess their dependency management strategies, while cybersecurity teams will face increased demands for monitoring and incident response. Industries such as fintech and e-commerce, heavily reliant on secure software, will need to enhance their security measures to mitigate risks associated with these vulnerabilities.
Why This Matters
This incident underscores a pivotal shift in the cybersecurity landscape, emphasizing the critical importance of supply chain security. As cyber threats become more sophisticated, CTOs and developers must adopt more rigorous verification processes for third-party packages. Implementing automated security checks and fostering a culture of security-first coding can significantly mitigate these risks.
As the threat landscape evolves, developers and organizations must remain vigilant against emerging malware tactics. Keeping abreast of security updates and fostering a strong security culture within teams will be essential. One key area to watch is the implementation of advanced dependency management tools that enhance security against such attacks.
Found this useful? Share it!