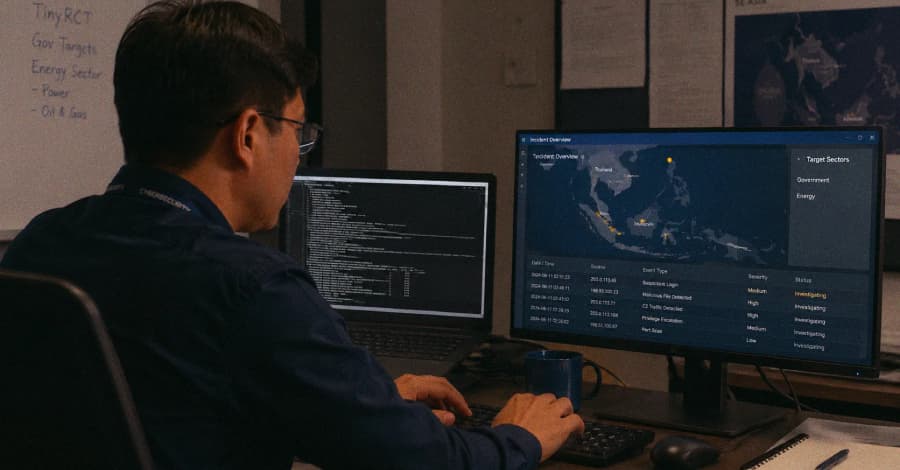
A Chinese-speaking advanced persistent threat (APT) actor has been linked to a new custom backdoor called TinyRCT as part of cyber attacks aimed at government entities and critical infrastructure in Southeast Asia. The activity, particularly aimed at state-owned enterprises in the energy and governm
Key Insights
10 editorial insights.
The recent deployment of the TinyRCT backdoor by a Chinese-speaking APT in Southeast Asia underscores the growing threat landscape targeting government entities and critical infrastructure. This incident highlights the vulnerabilities within state-owned enterprises, particularly in the energy sector, which are essential to national security and economic stability.
The involvement of a Chinese-speaking APT suggests a sophisticated group with significant resources, possibly linked to state-sponsored initiatives. This matters because it indicates a strategic intent to disrupt regional stability, particularly in countries like Vietnam and Indonesia, where energy dependence is critical for economic growth.
This development is strategically important as it signals an escalation in cyber warfare tactics aimed at destabilizing Southeast Asian nations. Given the geopolitical tensions in the region, such attacks could prompt governments to allocate more resources to cybersecurity, which may reshape national defense strategies and increase collaboration between nations.
The business impact of these cyber attacks on companies in Southeast Asia can be profound, leading to financial losses, data breaches, and reputational damage. For instance, state-owned energy firms could face substantial operational disruptions, which may hinder their ability to deliver services and fulfill contracts, affecting broader economic conditions.
This incident connects to a larger trend of increasing cyber threats targeting critical infrastructure observed over the last 12-24 months. As global reliance on digital systems grows, adversaries are increasingly exploiting vulnerabilities, with a reported 50% increase in cyber attacks on critical sectors such as energy and utilities during this period.
The cybersecurity market is projected to reach $345.4 billion by 2026, growing at a rate of 10.9% annually. As threats like TinyRCT emerge, organizations may feel pressured to invest more heavily in security solutions, potentially altering market dynamics and leading to increased competition among cybersecurity firms.
The primary risks posed by this new backdoor include potential data exfiltration and the compromise of critical infrastructure, leading to national security vulnerabilities. Additionally, there are unresolved questions regarding the extent of the breach and which entities have already been affected, which may lead to a ripple effect across the region.
Competitors in the cybersecurity industry are likely to respond by enhancing their threat detection and response capabilities, particularly for critical infrastructure. Companies such as Palo Alto Networks and CrowdStrike may increase their focus on Southeast Asia, offering tailored solutions to mitigate risks posed by APTs and similar threats.
In the next 6-12 months, key regulatory milestones to watch include potential new cybersecurity laws or frameworks established by Southeast Asian countries. This may involve collaboration with international partners to enhance threat intelligence sharing and to develop more robust defense mechanisms against state-sponsored cyber threats.
For technology professionals and investors, the emergence of the TinyRCT backdoor signifies a critical need to prioritize cybersecurity investments and strategies. As the threat landscape evolves, organizations must adapt swiftly, and failure to do so could lead to significant financial repercussions and lost market credibility.
A new wave of cyber attacks targeting Southeast Asian government entities has emerged, attributed to a Chinese-speaking advanced persistent threat (APT) actor deploying a sophisticated backdoor known as TinyRCT. This development is crucial as it highlights vulnerabilities within critical infrastructure sectors, particularly those related to energy and governance, raising alarms about national security in the region.
The TinyRCT backdoor operates with advanced stealth capabilities, allowing attackers to infiltrate systems undetected. This backdoor employs custom protocols and encrypts its communications, making it difficult for traditional security solutions to identify malicious activities. The malware can relay sensitive information back to the APT actors, while simultaneously enabling remote control over infected systems. This level of sophistication indicates a significant leap in the tactics employed by threat actors, posing a formidable challenge for cybersecurity professionals tasked with safeguarding sensitive governmental data.
In the broader context, this incident underscores the increasing sophistication of cyber threats in Southeast Asia, particularly against state-owned enterprises. As competition intensifies among nations to secure critical infrastructure, investments in cybersecurity have surged. Reports indicate that spending on cybersecurity solutions in the region is projected to exceed $10 billion by 2025. With escalating threats from both state and non-state actors, businesses are compelled to enhance their cybersecurity frameworks to mitigate risks, leading to a rapidly evolving security landscape.
For the Indian tech ecosystem, the implications of these cyber attacks are significant. Indian IT firms, especially those involved in cybersecurity, may see increased demand for their services as Southeast Asian countries look to bolster their defenses. Additionally, companies that operate transnationally or have partnerships in the region may need to reassess their security protocols to ensure compliance and protection against similar threats. This heightened awareness could spur collaboration among Indian cybersecurity firms and Southeast Asian governments to develop more robust security solutions tailored to regional needs.
Key Highlights
- Chinese APT actors have deployed the TinyRCT backdoor in attacks.
- TinyRCT utilizes advanced encryption and stealth techniques.
- Projected cybersecurity spending in Southeast Asia to surpass $10 billion by 2025.
- Indian cybersecurity firms likely to benefit from increased demand for services.
- Expect heightened cybersecurity collaboration between India and Southeast Asia.
Real-World Impact
The immediate effects of these cyber attacks are profound, particularly for government IT departments and critical infrastructure operators. Roles such as cybersecurity analysts, IT managers, and compliance officers will face heightened pressure to reassess security protocols and implement advanced monitoring systems. Additionally, industries reliant on secure data management, including energy and finance, may experience increased scrutiny and regulatory changes as a response to these breaches.
Why This Matters
This incident signifies a crucial shift in the cyber threat landscape, highlighting the need for organizations to adopt a proactive cybersecurity posture. CTOs and developers must prioritize the integration of advanced threat detection and response capabilities into their systems. As attacks become more sophisticated, traditional security measures may no longer suffice, necessitating the adoption of innovative solutions and ongoing employee training to recognize and mitigate emerging threats.
Looking ahead, the evolution of the TinyRCT backdoor will be critical to monitor, especially as attackers refine their techniques. Organizations must remain vigilant and adapt to these changes, ensuring that their cybersecurity strategies evolve in tandem with the threats they face.
Found this useful? Share it!