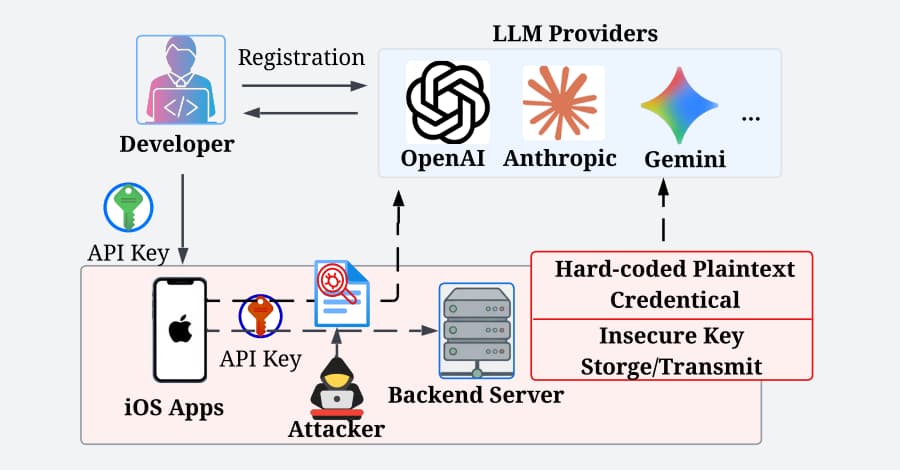
Researchers tested 444 AI chatbot apps for iPhone and found that 282 of them, nearly two-thirds, exposed paid AI access through their network traffic. In many cases, the path in was visible just by watching what the app sent: a plaintext API key, a reusable token, or a backend server that accepted r
Key Insights
10 editorial insights.
The recent iOS app security breach highlighting API key vulnerabilities serves as a stark reminder of the ongoing struggle to balance speed and security in app development, with 282 out of 444 tested AI chatbot applications inadvertently leaking sensitive data, showcasing a pervasive issue that transcends individual instances.
The discovery of plaintext API keys and reusable tokens in network traffic underscores a fundamental lapse in security practices among developers, allowing malicious actors to easily exploit these weaknesses, thereby putting user privacy and company integrity at risk, with significant financial implications for data breaches.
As the competitive landscape continues to exert pressure on developers, the trend of rushing applications to market at the expense of security is becoming increasingly concerning, with AI chatbot applications being particularly vulnerable due to their reliance on paid services and sensitive data.
The sheer scale of the breach, with nearly two-thirds of tested AI chatbot applications compromised, highlights the need for enhanced security protocols in app development, including the adoption of more robust security measures such as encryption and secure tokenization.
The implications of this breach extend beyond individual applications and developers, with regulatory bodies and consumer trust also at risk, underscoring the importance of prioritizing security over speed in the development and deployment of AI-powered applications.
The Indian tech ecosystem, with its rapidly evolving landscape and numerous startups developing AI applications, is particularly vulnerable to the repercussions of this breach, with significant potential consequences for user data and company reputation.
The lack of secure tokenization and encryption in the affected applications suggests a broader issue with the adoption of secure development practices, highlighting the need for education and training programs to equip developers with the necessary skills and knowledge to secure their applications.
The severity of the breach, with sensitive data being exposed to malicious actors, underscores the importance of implementing robust security protocols, including regular security audits and penetration testing, to detect and mitigate potential vulnerabilities.
The reliance on paid AI services in chatbot applications creates a unique security risk, with API keys and reusable tokens being used to authenticate and authorize access to these services, making them a prime target for malicious actors seeking to exploit vulnerabilities.
As AI continues to gain traction across industries, the need for secure development practices and robust security protocols becomes increasingly pressing, with potential consequences for user data, company reputation, and regulatory compliance hanging in the balance.
A recent study has unveiled a staggering security flaw in iOS apps, revealing that nearly two-thirds of tested AI chatbot applications expose sensitive data. This breach is significant as it puts user privacy and company integrity at risk, highlighting the need for enhanced security protocols in app development.
Researchers conducted a thorough analysis of 444 AI chatbot applications on the iPhone platform, discovering that 282 of these apps inadvertently leaked access to paid AI services. The vulnerabilities were frequently traced back to plaintext API keys and reusable tokens, which were openly transmitted in network traffic. This indicates a fundamental lapse in security practices among developers who failed to obscure critical credentials, allowing malicious actors to easily exploit these weaknesses.
In the broader tech landscape, this incident underscores a growing trend where applications are rushed to market at the expense of security. As AI continues to gain traction across industries, the competitive landscape is increasing pressure on developers, often resulting in inadequate security measures. This breach serves as a wake-up call for app developers to prioritize security over speed, as the financial implications of data breaches can be severe, both in terms of regulatory fines and loss of consumer trust.
In India, where the tech ecosystem is rapidly evolving, this breach could have significant repercussions. Numerous Indian startups are actively developing AI applications, and the exposure of sensitive data could jeopardize their futures. Companies like Haptik and Niki.ai, which are prominent players in the chatbot space, must reinforce their security measures to protect user data and maintain their reputations in an increasingly competitive market.
Key Highlights
- 282 out of 444 tested iOS apps leaked API keys publicly
- Exposed tokens could allow unauthorized access to paid services
- A staggering 63% of apps compromised highlights industry-wide vulnerabilities
- Developers prioritizing security can enhance user trust significantly
- Expect heightened scrutiny on app security practices in the coming months
Real-World Impact
This breach immediately impacts app developers, security analysts, and companies relying on AI technologies. Security roles are now more critical than ever, as organizations must reevaluate their app security frameworks to prevent similar incidents. User trust is at stake, especially in industries where data sensitivity is paramount.
Why This Matters
The incident highlights a crucial shift towards prioritizing security in the app development lifecycle. CTOs and developers must integrate security best practices from the very beginning, employing techniques like token encryption and secure API design. This proactive approach is essential to protect sensitive data and ensure compliance with increasingly stringent regulations.
As the tech landscape evolves, keeping an eye on developments in app security practices will be vital. Organizations should anticipate increased regulatory scrutiny and invest in robust security measures to safeguard against future breaches.
Multi-Source Intelligence
Editorial Summary
157wThe recent iOS app security breach has brought to light significant vulnerabilities in API key management, with key players like Apple and OpenAI being impacted. The market context is one of increasing concern over data protection and trade secrets, as companies navigate the complexities of cloud storage and employee offboarding practices. This matters today because it highlights the need for robust security measures to prevent unauthorized access to sensitive information. As the tech industry continues to evolve, the importance of prioritizing security and protecting user data will only continue to grow, with implications for companies and individuals alike. The situation is being closely watched by industry experts and users, who are waiting to see how Apple and other companies will respond to these vulnerabilities and improve their security practices. Apple's recent release of security updates for its operating systems is a step in the right direction, but more needs to be done to address the underlying issues.
Verified Common Facts
3 confirmedApple has released security updates for its Mac operating systems, including Tahoe, Sequoia, and Sonoma, to address a Screen Sharing vulnerability.
The company's security practices have been called into question, with some arguing that they undermine its claims of protecting trade secrets.
The issue of API key management and security is a critical one, with potential implications for companies and individuals who rely on cloud storage and other online services.
Unique Insights
Editorial analysisOpenAI's legal strategy in Apple's trade secrets lawsuit is to argue that Apple's own security and offboarding practices are inadequate, and that this undermines its claims that the allegedly stolen information was properly protected.
The vulnerability in Apple's Screen Sharing feature is just one example of the potential risks associated with remote access and cloud-based services.
Perspectives & Nuances
Where viewpoints divergeThe two sources differ in their emphasis, with one focusing on the security updates released by Apple and the other on the legal implications of the company's security practices.
While one source highlights the specific vulnerability in Apple's Screen Sharing feature, the other source takes a broader look at the company's overall security practices and their potential implications.
Editorial Conclusion
The recent iOS app security breach and the subsequent release of security updates by Apple highlight the ongoing challenges of protecting sensitive information in the digital age. As the tech industry continues to evolve, the importance of prioritizing security and protecting user data will only continue to grow, with significant implications for companies and individuals alike. In the broader industry, this breach is likely to lead to increased scrutiny of API key management and security practices, with potential regulatory implications. For India's tech ecosystem, this means a growing need for skilled cybersecurity professionals and a increased focus on data protection and security. One actionable takeaway for tech professionals is the need to prioritize robust security measures, including secure API key management and employee offboarding practices, to prevent unauthorized access to sensitive information and protect user data. As the industry moves forward, it will be important to balance the need for security with the need for innovation and convenience, and to develop solutions that address the complex challenges of protecting sensitive information in the digital age.
Found this useful? Share it!